
Private-Credit FinTech: 30% Lower AWS Spend, Zero Public Endpoints and a MAS TRM-Ready Platform
HiFX rebuilt an organically grown AWS estate for a Southeast Asian private-credit FinTech into a segmented, Terraform-managed, zero-trust architecture in just three weeks.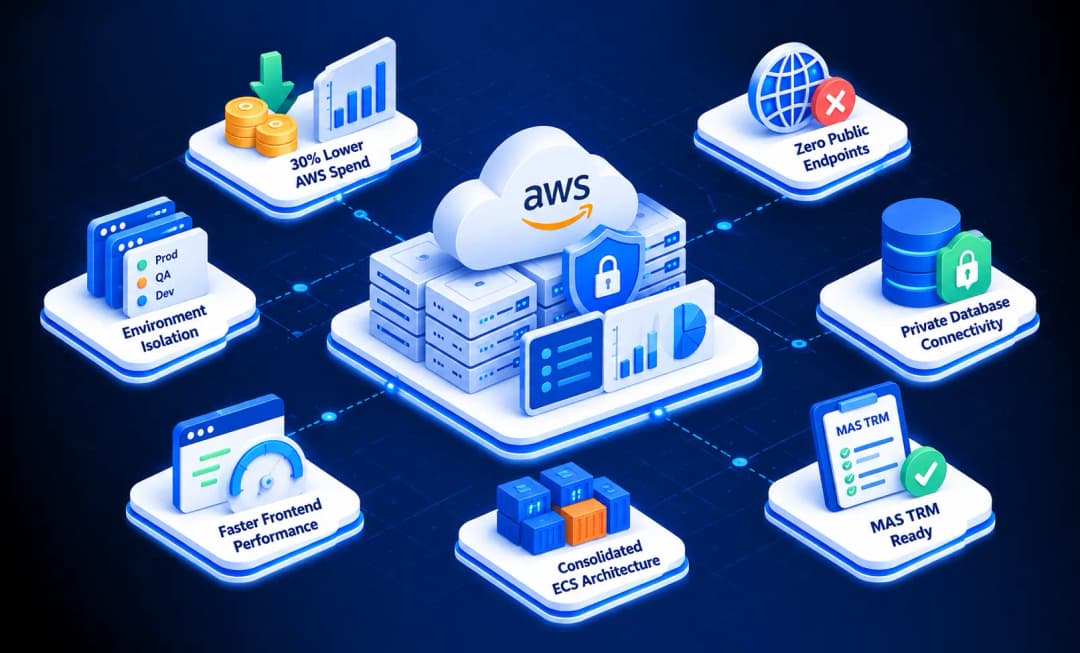
 30% Lower AWS Spend
 Zero Public Non-Production Endpoints
 42% Faster Frontend Load Times
 100% Infrastructure as Code
The platform had scaled faster than its infrastructure. As the client prepared for alignment with the Monetary Authority of Singapore's Technology Risk Management (MAS TRM) Guidelines, six problems stood out.
One account for everything: Production, QA and development shared a single AWS account. A misconfigured IAM policy or a test script pointed at the wrong resource could reach production, costs could not be cleanly attributed, and an auditor would struggle to see environment separation.
An open database: MongoDB Atlas accepted connections from any network. For a lender holding sensitive borrower and credit data, this was the most serious finding.
Non-production on the public internet: Dev and QA endpoints, including admin interfaces, were reachable from the internet and protected mainly by IP whitelists, which are brittle to maintain and weak as a control.
Fragmented compute: Microservices ran across 10+ ECS clusters, each with its own load balancer. Most ran well below capacity, and the client was paying for 10+ mostly idle ALBs.
Frontends on servers: Static web apps were served from containers with no CDN. Users in different regions saw inconsistent load times, and compute was being spent on serving files.
No consistent build process: Infrastructure was partly created by hand, so Dev, QA and Production had drifted apart, and changes could not be reliably reviewed or repeated.
 Environment isolationPrivate database connectivityZero-trust internal accessAWS cost optimisationGlobal frontend performanceMAS TRM compliance readiness
Rebuilding the AWS Estate for Security, Cost and Compliance
HiFX assessed the existing estate, designed a target architecture and migrated a live platform covering 4 backend microservices, 2 customer portals, 1 admin portal and data processing engines across Dev, QA and Production.1. Environment Isolation & AWS Account Segmentation
A separate AWS account was created for non-production environments under the same AWS Organization, with dedicated VPCs for Development, QA and Production. A mistake in Dev can no longer touch Production. Each account has its own IAM boundary and billing, and auditors can see environment separation directly in the account structure.2. Private Database Connectivity
We established VPC peering between MongoDB Atlas and each environment's VPC and removed public access from the Atlas IP access list. Only approved VPC CIDR ranges can connect, and database traffic no longer crosses the public internet.3. Consolidated Compute and a Single Entry Point
We collapsed 10+ ECS clusters into one shared ECS cluster per environment on EC2 capacity, managed by ECS Capacity Providers with auto-scaling. A single Multi-AZ Application Load Balancer with host-based routing replaced 10+ separate load balancers. Each microservice keeps its own task IAM role, security group and resource limits, so services share hardware without sharing permissions.4. Static Frontends on S3 and CloudFront
Web portals and dashboards moved off containers onto Amazon S3, served globally through Amazon CloudFront. Origin Access Control ensures buckets can only be read through CloudFront, and HSTS, Content-Security-Policy and X-Frame-Options headers are enforced at the edge.5. Zero-Trust Access with Cloudflare
Cloudflare Zero Trust replaced the initial Tailscale setup. cloudflared connectors run inside private subnets and make outbound-only encrypted tunnels to Cloudflare, so no inbound ports are opened. Engineers sign in through Cloudflare Access SSO, access is granted per application and per identity, and every session is logged.6. Everything as Code
All infrastructure is defined in Terraform and changed through GitHub pull requests. The same modules build Dev, QA and Production, so environments no longer drift, and every peer-reviewed change gives the client an audit trail for change management.Key Design Decisions
- Cloudflare Zero Trust over Tailscale: per-application policies tied to the identity provider, browser-based access for non-engineers and a per-request audit log for MAS TRM auditors.
- VPC peering over PrivateLink for Atlas: a private, CIDR-restricted path that cost less and was simpler to run at the client's current scale, with room to move to PrivateLink later.
- Shared ECS on EC2 over Fargate: steady, predictable workloads are significantly cheaper on packed EC2 capacity, with isolation kept at the account, service and resource layers.
- One ALB instead of many: a single place to attach WAF rules, TLS policy and logging, well within listener-rule limits.
- AWS WAF and Cloudflare together: AWS WAF protects public traffic at CloudFront and the ALB, while Cloudflare handles identity-based access to private resources.
How We Delivered It
- Phased migration: non-production environments were migrated and validated first, followed by production.
- A single Terraform codebase with environment-specific variable files provisioned every environment consistently.
- MongoDB Atlas moved to private VPC connectivity without disrupting application services.
- Each stage was validated through application health and infrastructure monitoring, with the existing setup retained for safe rollback.
- AWS account segmentation
- Private MongoDB Atlas peering
- Shared ECS on EC2 with one ALB
- S3 + CloudFront static frontends
- Cloudflare Zero Trust access
- Terraform via GitHub pull requests
Measurable Results
In three weeks, the client moved from an organically grown AWS estate to a cheaper, faster and auditable platform ready for MAS TRM alignment.30% Lower AWS Spend
Monthly AWS infrastructure spend fell from $2,300 to $1,600 by consolidating 10+ ECS clusters and 10+ ALBs into one of each per environment, and removing web-server compute for static frontends.Zero-Trust Security
- Zero publicly reachable non-production endpoints
- MongoDB Atlas reachable only from approved VPC CIDRs over private peering
- Inbound security-group rules on private resources restricted
Faster Frontends
Frontend load time across Southeast Asia dropped from 5,000 ms to 2,900 ms, with static apps served from nearby CloudFront edge locations and zero web servers.MAS TRM Ready
Control gaps across network, access and logging were closed, and every environment is now managed as code in Terraform with a peer-reviewed change history.Technologies we Used

Transforming Businesses Through Technology
Mobile Application & Admin Panel
HiFX designed and developed a scalable mobile application and centralized admin panel for a leading national bakery and café chain, simplifying operations and improving customer accessibility.
 ·
 ·
 ·
 ·
 ·

Lens
HiFX designed and developed a digital platform to simplify lens inventory management, improve operational efficiency, and enable real-time visibility across retail operations.
 ·
 ·
 ·
 ·
 ·

Payment Application
HiFX designed and developed a secure payment application to simplify digital transactions, improve operational efficiency, and deliver seamless payment experiences through scalable cloud-native infrastructure.
··
Single Sign On
HiFX designed and developed a centralized Single Sign-On solution to streamline authentication workflows, improve security, and deliver seamless access management across enterprise applications and platforms.
· ·
 ·
 ·
 ·